Supplier Risk Management Starts at Onboarding
Supplier risk management starts at onboarding. Score inherent risk and supplier reliability on one record before the first PO, then keep that record current.

Founder & Chief Executive Officer
- Published
- Updated
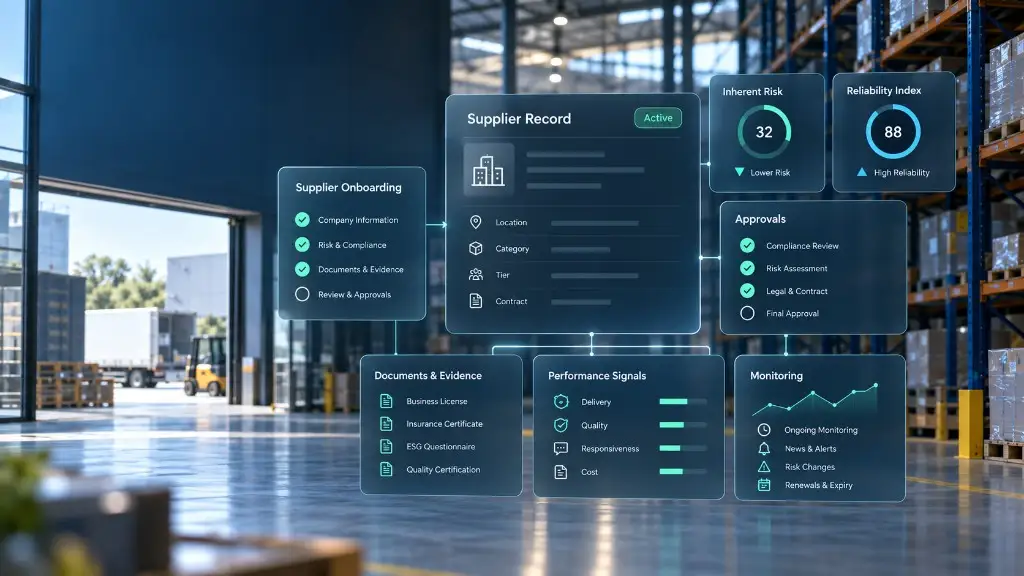
Supplier risk management starts at onboarding. Before the first purchase order, capture the inherent risk of the relationship and a view of supplier reliability on the same supplier identity you will use for performance, monitoring, and supplier responsibility reporting. AI can keep that record current. It cannot replace the decision that created it.
That sounds simple. In many organizations, it is not how the work is designed.
The purchasing system creates a vendor number so accounts payable can issue a payment. Legal collects a questionnaire in a separate workflow. A risk team maintains another file. Performance data arrives later from an ERP or a spreadsheet. Supplier diversity and CSR evidence often sits somewhere else again.
Each team may be doing its job. The organization still lacks one dependable record of the relationship.
Why the market built around purchasing: POs, invoices, and catalogs
Procurement software grew up around the transaction: purchase orders, invoices, catalogs, receipts, and payment. Those workflows matter, but they answer a narrow question: what should we buy, and how should we pay for it?
Supplier relationship management answers a wider question: can we rely on this relationship, and what should we do next?
The difference appears before a supplier is approved. A purchasing-first process can confirm a tax form, banking details, and a contract while leaving the relationship’s exposure undefined. The supplier then goes live with an incomplete record. Risk is assessed after the fact, if it is assessed at all, and performance is scored against an identity that may not include the original evidence.
This is why a risk program can look active while remaining reactive. It has questionnaires, alerts, and review meetings, but none of them starts with the decision the organization made when it accepted the supplier.
Inherent risk belongs in supplier onboarding
Inherent risk is the exposure the relationship carries before controls reduce it. It is not a prediction that a supplier will fail. It is the risk the buyer accepts by working with that supplier for a particular purpose.
At intake, the team can record the context that makes the relationship more or less consequential:
- Category and service: What the supplier provides, and how difficult it would be to replace.
- Geography: Where the supplier operates, produces, stores data, or depends on logistics.
- Criticality and concentration: What happens if the supplier stops performing, and how much of the business depends on one supplier, region, or sub-tier source.
- Evidence owed: Which certifications, controls, insurance documents, financial information, or policy attestations the relationship requires.
- Access and exposure: What systems, facilities, information, or regulated activity the supplier can reach.
Capturing those facts at onboarding changes the workflow. The organization can route the right depth of due diligence, assign an owner, and make an approval decision with the relationship’s context in view. The risk record is not created later by copying a vendor number into another system. It begins on the identity that will carry the relationship forward.
For teams improving an existing process, the first step is to map where those facts live today. Gainfront’s supplier onboarding workflow is designed around that handoff: intake, evidence, approvals, and the reusable supplier record belong together.
Reliability index: how we build it
A reliability index should answer an operational question: how dependable is this supplier to work with? It should help a buyer compare relationships, decide where attention belongs, and see when the relationship is changing.
It should not be a financial-distress scanner. Most suppliers an organization onboards will never experience a dramatic public financial event. If the index only lights up for insolvency headlines, it is quiet for the suppliers the business actually buys from.
The right inputs, weights, and thresholds depend on the operating model and risk appetite. The design principle is clear: the score needs evidence from the relationship, not a single headline. A team designing its model should decide how to connect four kinds of evidence:
- Relationship context: category, geography, criticality, concentration, access, and the obligations accepted at intake.
- Controls and evidence: questionnaires, certifications, contracts, policies, insurance, and the status of documents with an expiry date.
- Observed operations: delivery, quality, responsiveness, capacity, and the follow-through on corrective actions, when those signals are available.
- Change over time: monitoring events, incidents, reassessments, open findings, and whether the supplier’s position is improving or deteriorating.
The point is not to turn every signal into a mysterious number. A useful index makes the evidence legible. It shows what moved the score, who owns the next action, and which threshold changes the workflow. It also keeps the score attached to the onboarding identity, so a later performance update does not create a second supplier with a second history.
That is the role RiskMetrix plays in Gainfront’s model. Its risk workflow starts with the supplier’s first submission, carries the reliability view into the relationship, and keeps monitoring and mitigation on the same record. The supplier risk management solution describes the full risk lifecycle.
What has to live on one supplier record
One record does not mean one team owns every task. It means every team works from the same supplier identity and can see the context it needs.
At minimum, the record should connect:
- onboarding submissions and approvals
- inherent risk and the evidence behind it
- the reliability index and the reason it moved
- contracts, obligations, and renewal dates
- delivery, quality, responsiveness, and other performance measures
- monitoring findings, remediation tasks, and closure evidence
- supplier diversity, ESG, and CSR evidence
- spend, category, criticality, and concentration context
- the relationship owner, decision history, and next action
This connection is what makes the record useful at each stage. An onboarding manager can see what is missing before approval. A risk owner can see who is responsible for remediation. A category manager can read performance in the context of the risk the organization accepted. A CSR leader can report supplier evidence without maintaining a separate supplier list.
That holistic view is also where supplier diversity and responsibility work stops being a side file. Tier 1 and Tier 2 status, certifications, and impact evidence live on the identity that already holds risk and performance, so a diverse supplier is not maintained in one system and scored for reliability in another. A diversity or CSR lead can report supplier diversity spend and certification currency from the record the rest of the organization already uses, and read that evidence next to reliability instead of in a separate list.
It also gives the organization a practical answer to a common question: can we keep our current purchasing suite? Often, yes. The important test is whether onboarding can write a reusable identity and whether purchasing, risk, performance, and CSR systems can read the context they need. AgentFlow is Gainfront’s orchestration path for teams keeping the systems they already own. If the route is not part of your current stack, the SLM suite provides the broader shared record.
Inherent risk vs. a later questionnaire vs. a headlines feed
These tools can coexist, but they do different jobs.
| Mechanism | When it starts | What it tells you | What it cannot do alone |
|---|---|---|---|
| Inherent risk | At intake, before approval | What exposure the relationship carries in its context | It does not describe every control or future change |
| Questionnaire or assessment | During or after intake | What the supplier says and which evidence it provides | It is not a complete operating history |
| Reliability index | Before go-live and throughout the relationship | How dependable the supplier appears across the evidence available | It needs visible inputs, ownership, and thresholds |
| Headlines feed | When an external event is published | Whether a public event may affect a supplier | It misses quiet deterioration and most suppliers without headlines |
The sequence matters. Inherent risk sets the starting context. A questionnaire and due diligence update the evidence. Performance and monitoring update the relationship. The index gives operators a comparable view of dependability. A headlines feed can add a signal, but it cannot be the risk program.
How AI is changing supplier risk, and how it is not
AI does not turn a purchasing-first process into supplier relationship management. A model watching news on a vendor number that never held inherent risk is still reactive. It is faster at being late.
The change that matters is narrower. On a reusable onboarding identity, AI can read questionnaires, certificates, and intake documents onto the record operators will use later. Given the inherent-risk context, it can route a deeper review to the suppliers who need it instead of the same packet to everyone. Monitoring events, certification expiry, and vulnerability notices get logged against the reliability index. And when a threshold moves, a workflow opens with an owner and a due date.
It cannot invent the relationship context. It cannot replace the approval decision. And it cannot reconcile five supplier identities after the fact.
Gainfront’s EfficiencyAI layer evaluates unstructured evidence on that same ID. If a vendor’s AI cannot write to the onboarding identity, it is a headlines product with a new label.
A practical way to make onboarding risk-first
Most teams do not need to replace every system to change the starting point. They can make the first supplier record more useful, then expand from there.
1. Define the decision at intake
Write down what approval means for each supplier tier. The question is not only whether the form is complete. It is whether the organization understands the relationship it is about to accept, the evidence still owed, and the owner of the next step.
2. Route depth by context
An occasional office-services supplier should not receive the same process as a single-source supplier with operational, data, or regulatory exposure. Use category, geography, criticality, concentration, and access to determine which checks and reviewers apply.
3. Set the record up for later signals
Give performance, monitoring, contracts, and CSR teams a stable identity to reference. If each downstream system creates its own supplier, reconciliation becomes part of every review and no score can be trusted for long.
4. Make movement actionable
When evidence expires, performance changes, or monitoring finds an issue, the record should show the owner, due date, threshold, and decision. A score without a next action is a report. A score connected to workflow is a control.
5. Review the model with product and risk owners
Before publishing or operationalizing a reliability index, confirm its approved inputs, weights, thresholds, and terminology. Keep the model explainable to procurement, risk, legal, and the supplier itself. The index should support a decision, not obscure one.
FAQ for risk and operations teams
Where does inherent risk belong if Legal already runs questionnaires?
At intake, on the supplier identity that accounts payable and the operating teams will use. Questionnaires and due diligence update the score and its evidence. They do not replace the initial relationship context or justify a second risk file.
Why is financial distress not the core of a reliability index?
Most suppliers will not show a material public financial event. Dependability also appears in delivery, quality, responsiveness, capacity, evidence currency, concentration, and follow-through. An index that waits for a crisis is empty for the suppliers the business works with every day.
Can we keep Coupa, Ariba, or our ERP for purchasing?
Yes, if onboarding creates a reusable supplier identity and the systems exchange the context needed for risk, performance, and reporting. Keeping a purchasing suite does not make it a supplier relationship system. The test is whether the record carries risk before the first purchase order and remains usable afterward.
What is the difference between inherent risk and ongoing monitoring?
Inherent risk describes the relationship accepted at onboarding. Monitoring looks for change after that decision. Monitoring should update the same supplier record, so a new signal reaches the people who can act instead of arriving in a disconnected file.
Does AI replace scoring inherent risk at onboarding?
No. AI can read evidence and keep the reliability view current. The intake decision still belongs to the people accepting the relationship. If the model has no onboarding identity to write to, it is another feed.
What should we ask a supplier risk management software vendor?
Ask where inherent risk is scored, which identity receives the score, how the reliability index explains movement, and whether performance, contracts, CSR, and spend can read the same record. Ask whether any AI writes to that same identity or to a parallel dashboard. Also ask what happens when a threshold is crossed: who is notified, which workflow opens, and where closure evidence lives.
Make the supplier record dependable before the first PO
Risk-first SRM is an operating choice. Start with the relationship you are accepting, capture inherent risk on the onboarding record, and attach a reliability view that operators can explain and act on. Then let monitoring, performance, contracts, spend, and CSR build on that identity over time.
If you want to see where your current process fractures, use the Procurement Stack Scorecard. To discuss a supplier record that can replace or orchestrate the systems you already own, book a Gainfront demo.